---
title: Security Recommendations of Serverless Applications Deep Dive
description: Learn the latest AWS security best practices for serverless and AI workloads, focusing on environment isolation, encryption, IAM, and authentication strategies.
image: https://blog.ippon.tech/hubfs/Ippon%20copy-2.jpg
---
[Skip to main content](https://blog.ippon.tech/security-recommendations-of-serverless-applications-deep-dive#main)
[   ](https://ipponusa.com/)
- [Home](https://ipponusa.com)
- [Show submenu for About About](https://ipponusa.com/about-us)
- [Who We Are](https://ipponusa.com/who-we-are)
- [Careers](https://ipponusa.com/careers)
- [Show submenu for Our Partners Our Partners](https://ipponusa.com/our-partners/)
- [AWS](https://ipponusa.com/our-partners/aws/)
- [Snowflake](https://ipponusa.com/our-partners/snowflake/)
- [Databricks](https://ipponusa.com/our-partners/databricks/)
- [Microsoft](https://ipponusa.com/our-partners/microsoft/)
- [Show submenu for Services Services](https://ipponusa.com/services)
- [Snowflake](https://ipponusa.com/service/snowflake-concierge/)
- [Artificial Intelligence](https://ipponusa.com/service/artificial-intelligence/)
- [Data & Analytics](https://ipponusa.com/service/data-analytics/)
- [Cloud Strategy](https://ipponusa.com/service/cloud-strategy/)
- [Platform Modernization](https://ipponusa.com/service/platform-moderization/)
- [Product Innovation](https://ipponusa.com/service/product-innovation/)
- [Operating Model](https://ipponusa.com/service/operating-model/)
- [Blogs](https://blog.ippon.tech/)
- [Success Stories](https://ipponusa.com/success-stories/)
- [Show submenu for Resources Resources](https://ipponusa.com/resources/)
- [eBooks](https://ipponusa.com/ebooks/)
- [The Data Pour](https://info.ippon.tech/the-data-pour)
- [Videos & Webinars](https://info.ippon.tech/videos-and-webinars)
- [Media Center](https://ipponusa.com/media-center/)
Search
Open main navigation
Close main navigation
- [Home](https://ipponusa.com)
- Show submenu for About About
- About
- [About](https://ipponusa.com/about-us)
- [Who We Are](https://ipponusa.com/who-we-are)
- [Careers](https://ipponusa.com/careers)
- Show submenu for Our Partners Our Partners
- Our Partners
- [Our Partners](https://ipponusa.com/our-partners/)
- [AWS](https://ipponusa.com/our-partners/aws/)
- [Snowflake](https://ipponusa.com/our-partners/snowflake/)
- [Databricks](https://ipponusa.com/our-partners/databricks/)
- [Microsoft](https://ipponusa.com/our-partners/microsoft/)
- Show submenu for Services Services
- Services
- [Services](https://ipponusa.com/services)
- [Snowflake](https://ipponusa.com/service/snowflake-concierge/)
- [Artificial Intelligence](https://ipponusa.com/service/artificial-intelligence/)
- [Data & Analytics](https://ipponusa.com/service/data-analytics/)
- [Cloud Strategy](https://ipponusa.com/service/cloud-strategy/)
- [Platform Modernization](https://ipponusa.com/service/platform-moderization/)
- [Product Innovation](https://ipponusa.com/service/product-innovation/)
- [Operating Model](https://ipponusa.com/service/operating-model/)
- [Blogs](https://blog.ippon.tech/)
- [Success Stories](https://ipponusa.com/success-stories/)
- Show submenu for Resources Resources
- Resources
- [Resources](https://ipponusa.com/resources/)
- [eBooks](https://ipponusa.com/ebooks/)
- [The Data Pour](https://info.ippon.tech/the-data-pour)
- [Videos & Webinars](https://info.ippon.tech/videos-and-webinars)
- [Media Center](https://ipponusa.com/media-center/)
- Search
- [Contact Us](https://ipponusa.com/contact/)
[Contact Us](https://ipponusa.com/contact/)
# Security Recommendations of Serverless Applications Deep Dive

by [Iryna Chmelyk](https://blog.ippon.tech/author/iryna-chmelyk)
December 8, 2025
## Introduction
The “Implementing security best practices for serverless applications” session at re:Invent was a very useful talk for anyone interested in running regular serverless and agentic AI workloads on AWS. It also validated that the security patterns Ippon teams are recommending and implementing for our clients are fully aligned with the latest AWS guidance and current best practices.
## Current Security Best Practices for Serverless Applications
**Environment isolation with AWS accounts**
Using separate AWS accounts for product environments (dev, test, and prod) creates hard isolation boundaries that limit blast radius and reduce the risk of accidental cross-environment access. It also lets teams apply consistent guardrails at the OU/account level.
**Encryption at rest and in transit**
Encrypting all data at rest with KMS-backed keys and enforcing TLS in transit ensures that even if data is accessed outside intended paths, it remains protected and auditable. This is critical for both regulatory requirements and for defending against credential leaks, misconfigurations, and interception on the wire. Some AWS services encrypt data by default, while others require you to turn encryption on explicitly, so it’s important to double-check each service’s settings to ensure encryption is properly enabled everywhere.
**Layered IAM with no wildcards**
The session reinforced a “defense in depth” approach to IAM, specifically SCPs for organization-wide guardrails, resource policies on services like Lambda, API Gateway, S3, VPC endpoints, and KMS keys, plus tightly scoped IAM principal and session policies as well as permissions boundaries. Avoiding "\*" in actions, resources, and principals is not just theory; it directly reduces the impact of compromised credentials or bugs by ensuring identities can only do exactly what they need.
**Lambda execution roles and resource-based policies**
Giving each Lambda function a dedicated, minimal execution role and using resource-based policies to control who can invoke it turns identity into a precise perimeter. This prevents lateral movement between functions and services and makes permissions easier to review over time as serverless systems evolve.
**Detection and runtime visibility (Inspector and GuardDuty)**Amazon Inspector provides automated scanning of code and dependencies so known vulnerabilities are caught before deployment, which is critical in fast-moving serverless pipelines. Amazon GuardDuty then monitors for suspicious activity and runtime anomalies across accounts, filling the observability gap that traditional host-based agents can’t cover in serverless environments.
**Input validation and edge protection**
Validating untrusted payloads at API Gateway and again inside Lambda (for example, with the Powertools validation library) stops malformed or malicious data before it can reach core logic. Adding AWS WAF in front of public-facing endpoints, with AWS-managed and custom rules, provides an extra shield against common web exploits, bots, and abuse patterns that would otherwise hit your APIs directly.
## Authorization Best Practices
**Cognito vs. Lambda authorizers + Verified Permissions**
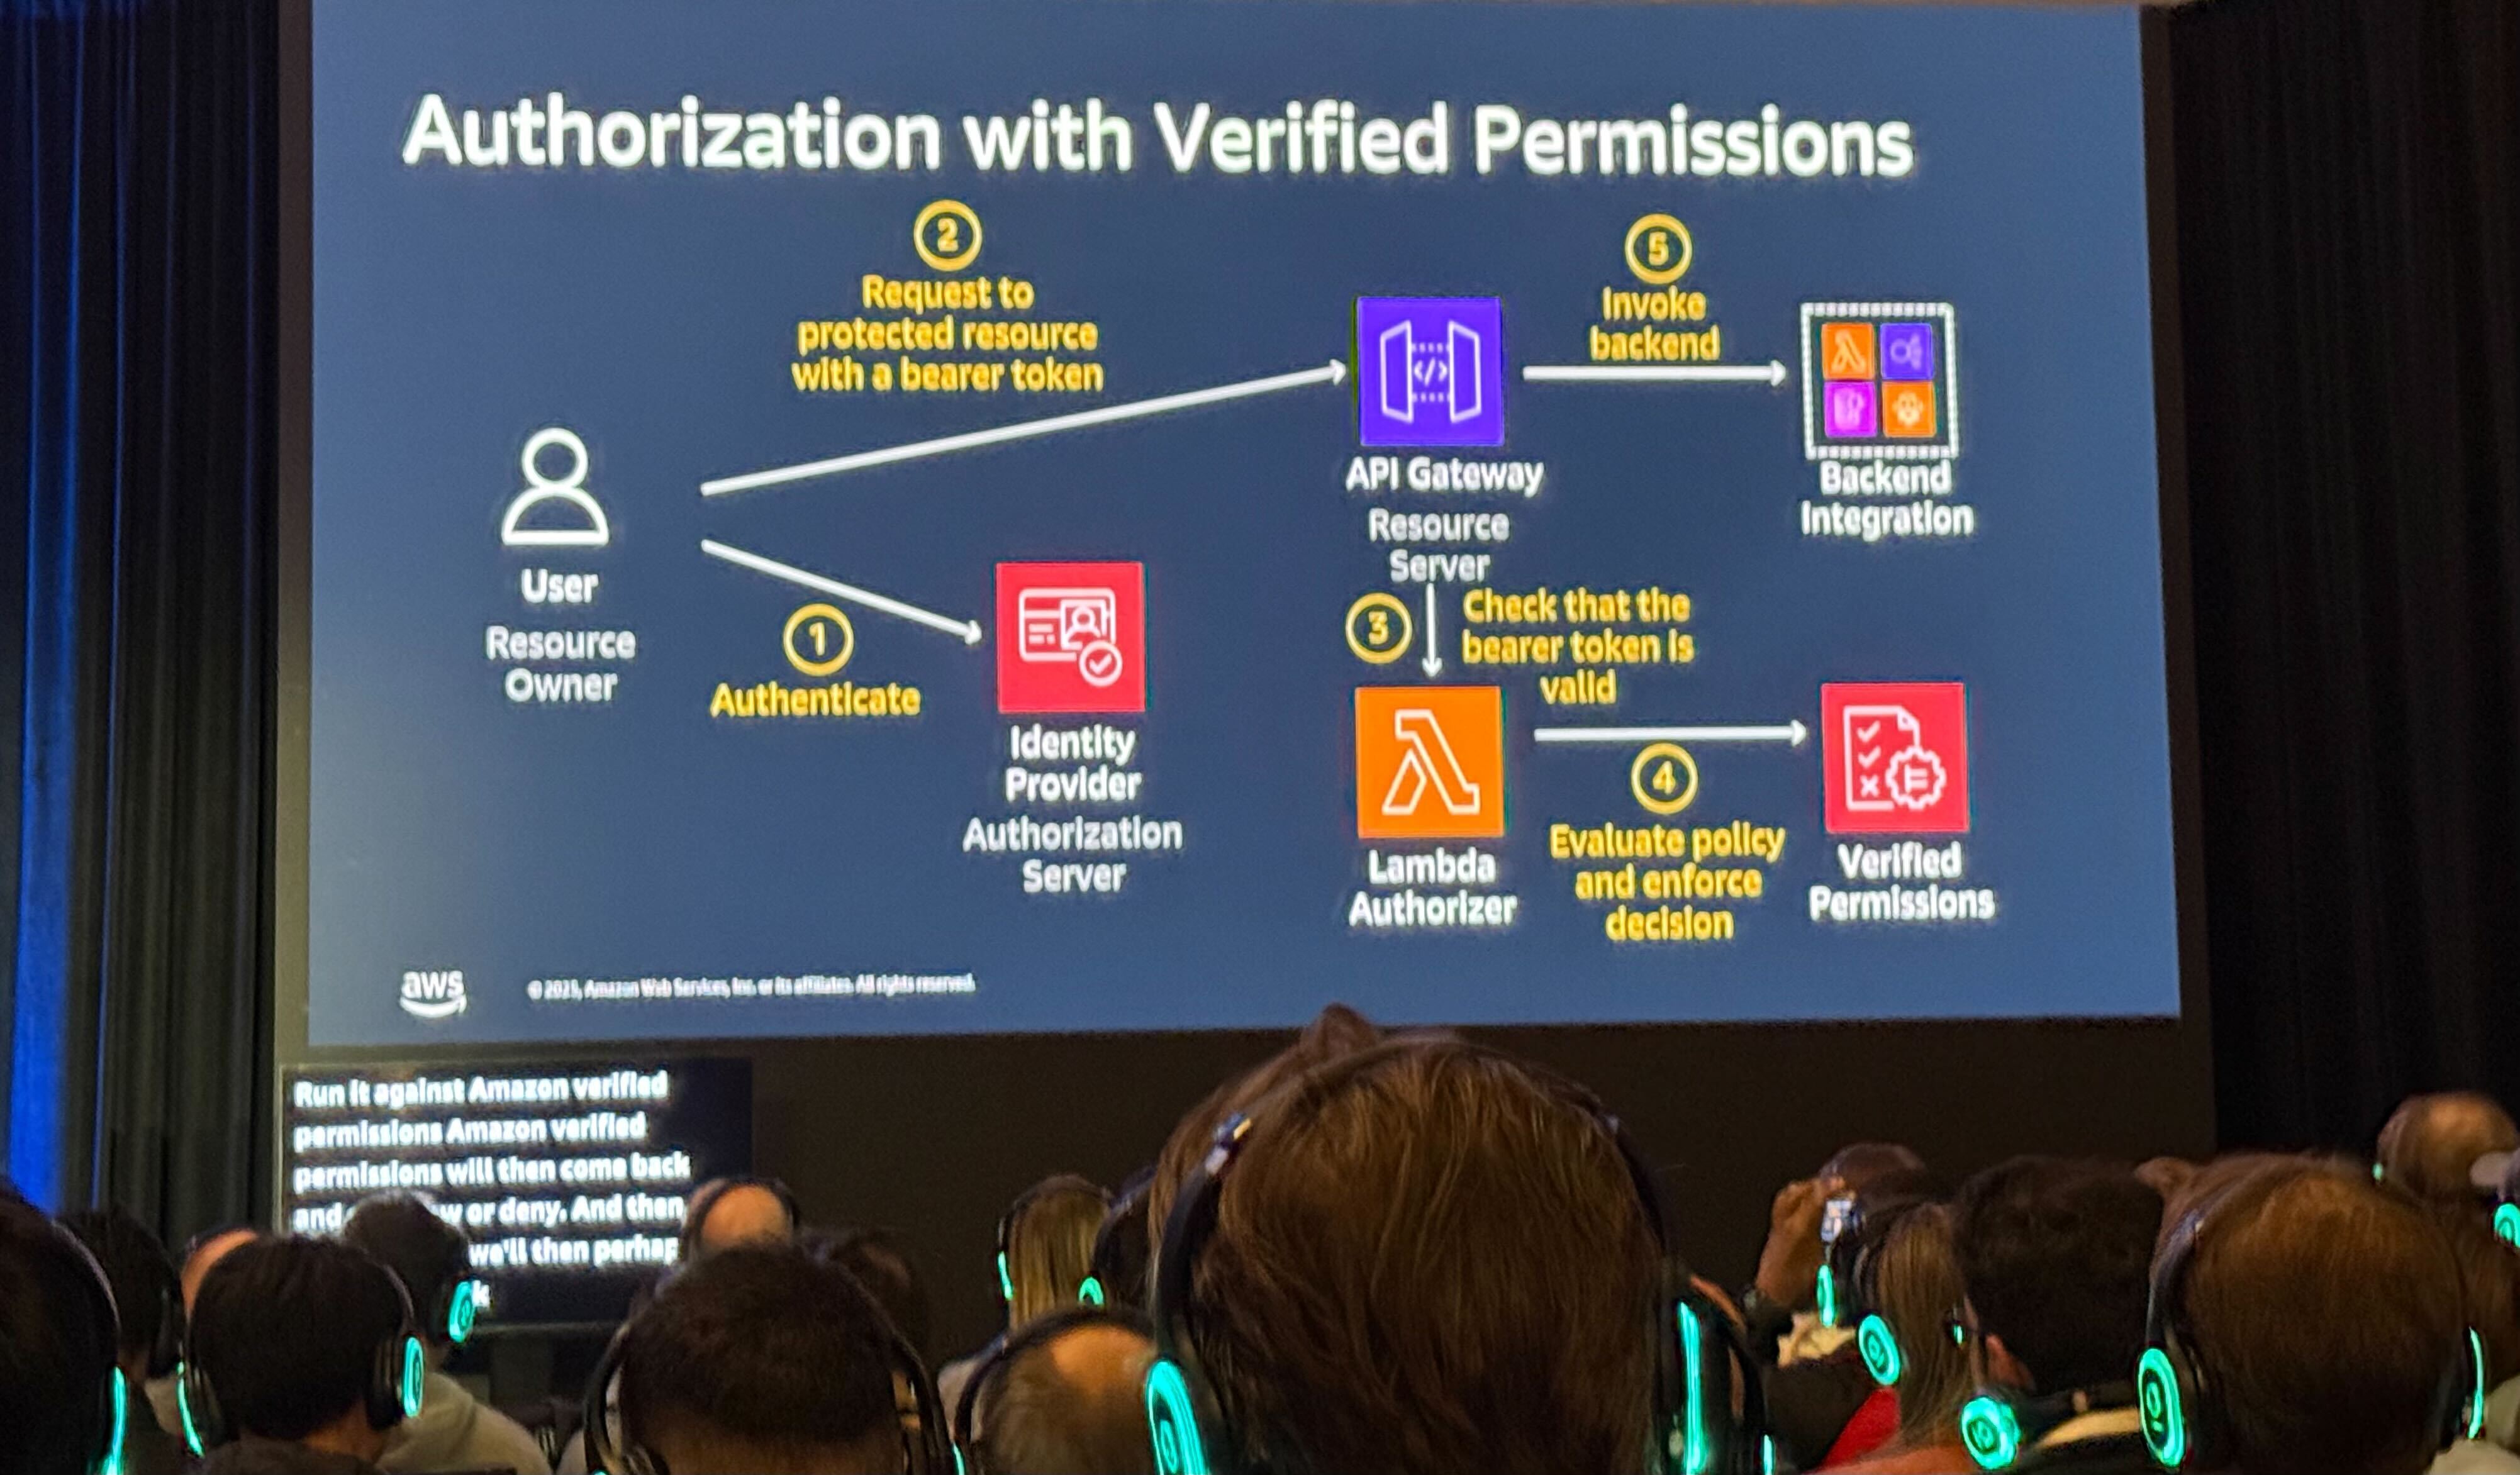
Using Cognito or an external OIDC provider for user authentication, then choosing between Cognito authorizers and Lambda authorizers based on how much custom logic is needed, cleanly separates identity from application code. Layering Amazon Verified Permissions on top, with Cedar policies, enables fine-grained, context-aware authorization that can be tested, audited, and evolved without rewriting Lambdas.
**OAuth2 Grant Types for serverless and agentic AI**
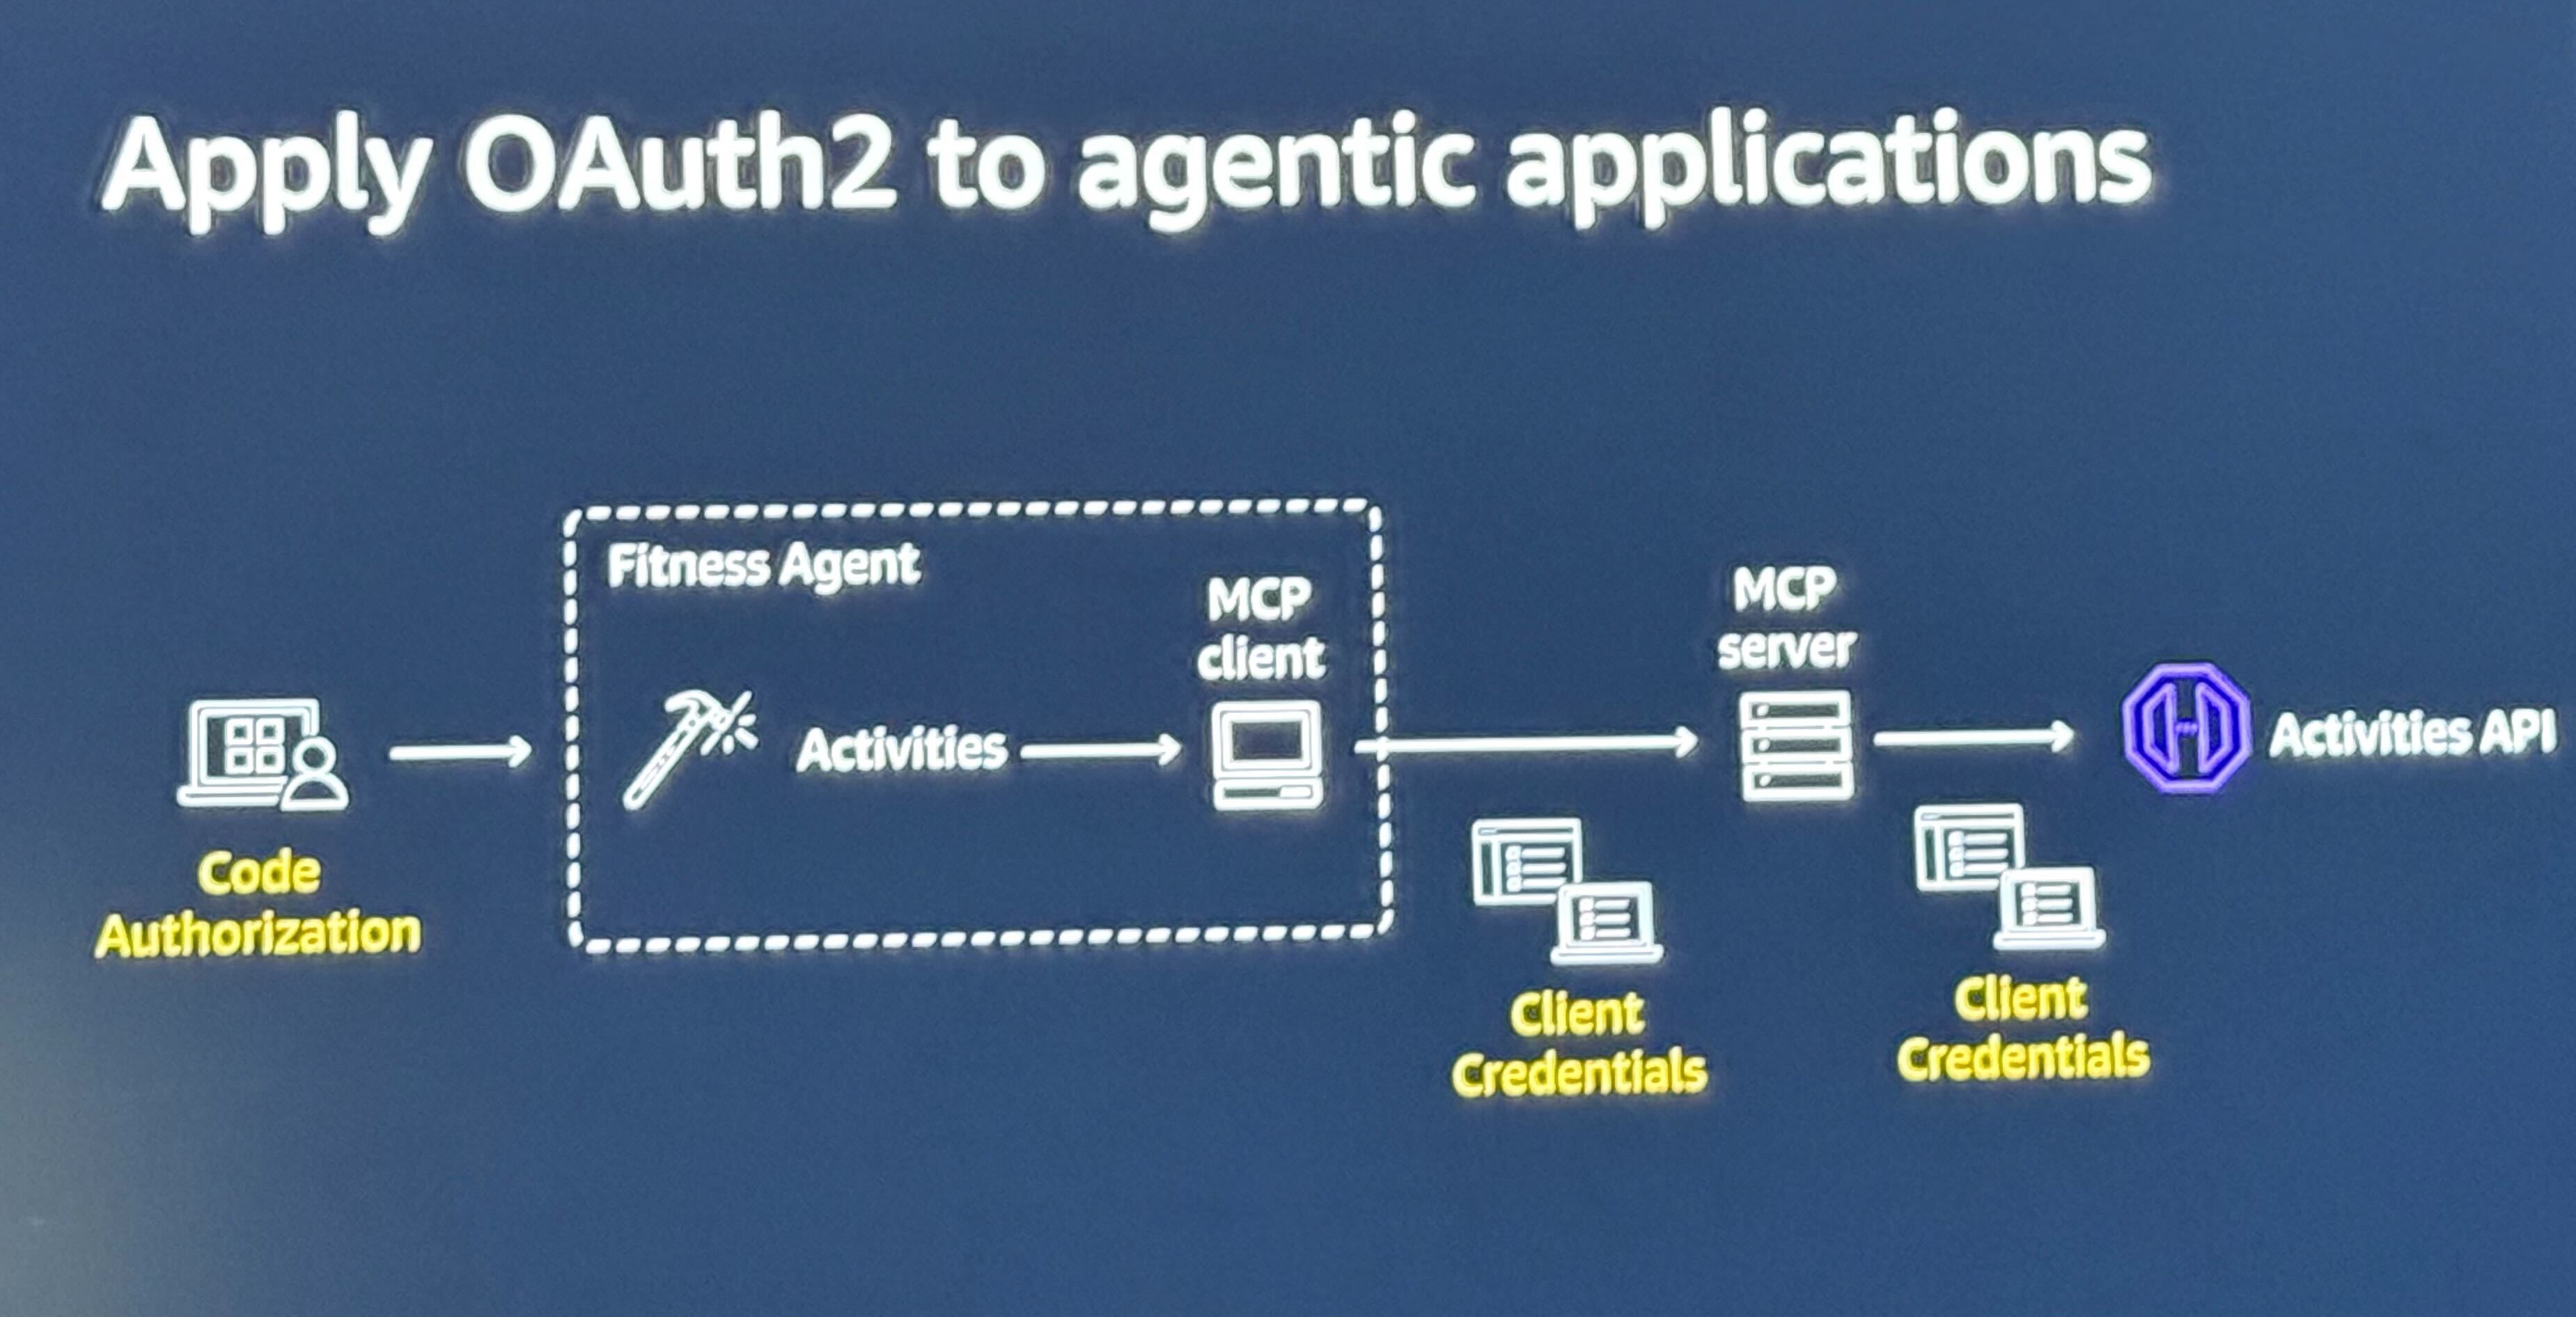
The session focused on the two OAuth2 grant types that really matter in these architectures: authorization code for user-facing serverless applications and client credentials for machine-to-machine (M2M) and agent-to-API scenarios. The topic of M2M communication becomes critical in agentic AI workloads, where agents often act as the “system” using client credentials to call downstream APIs, while frontends rely on the authorization code flow to maintain strong user identity and consent. This is how the flow looks.
## Auth with AgentCore Identity
**Inbound and outbound auth**
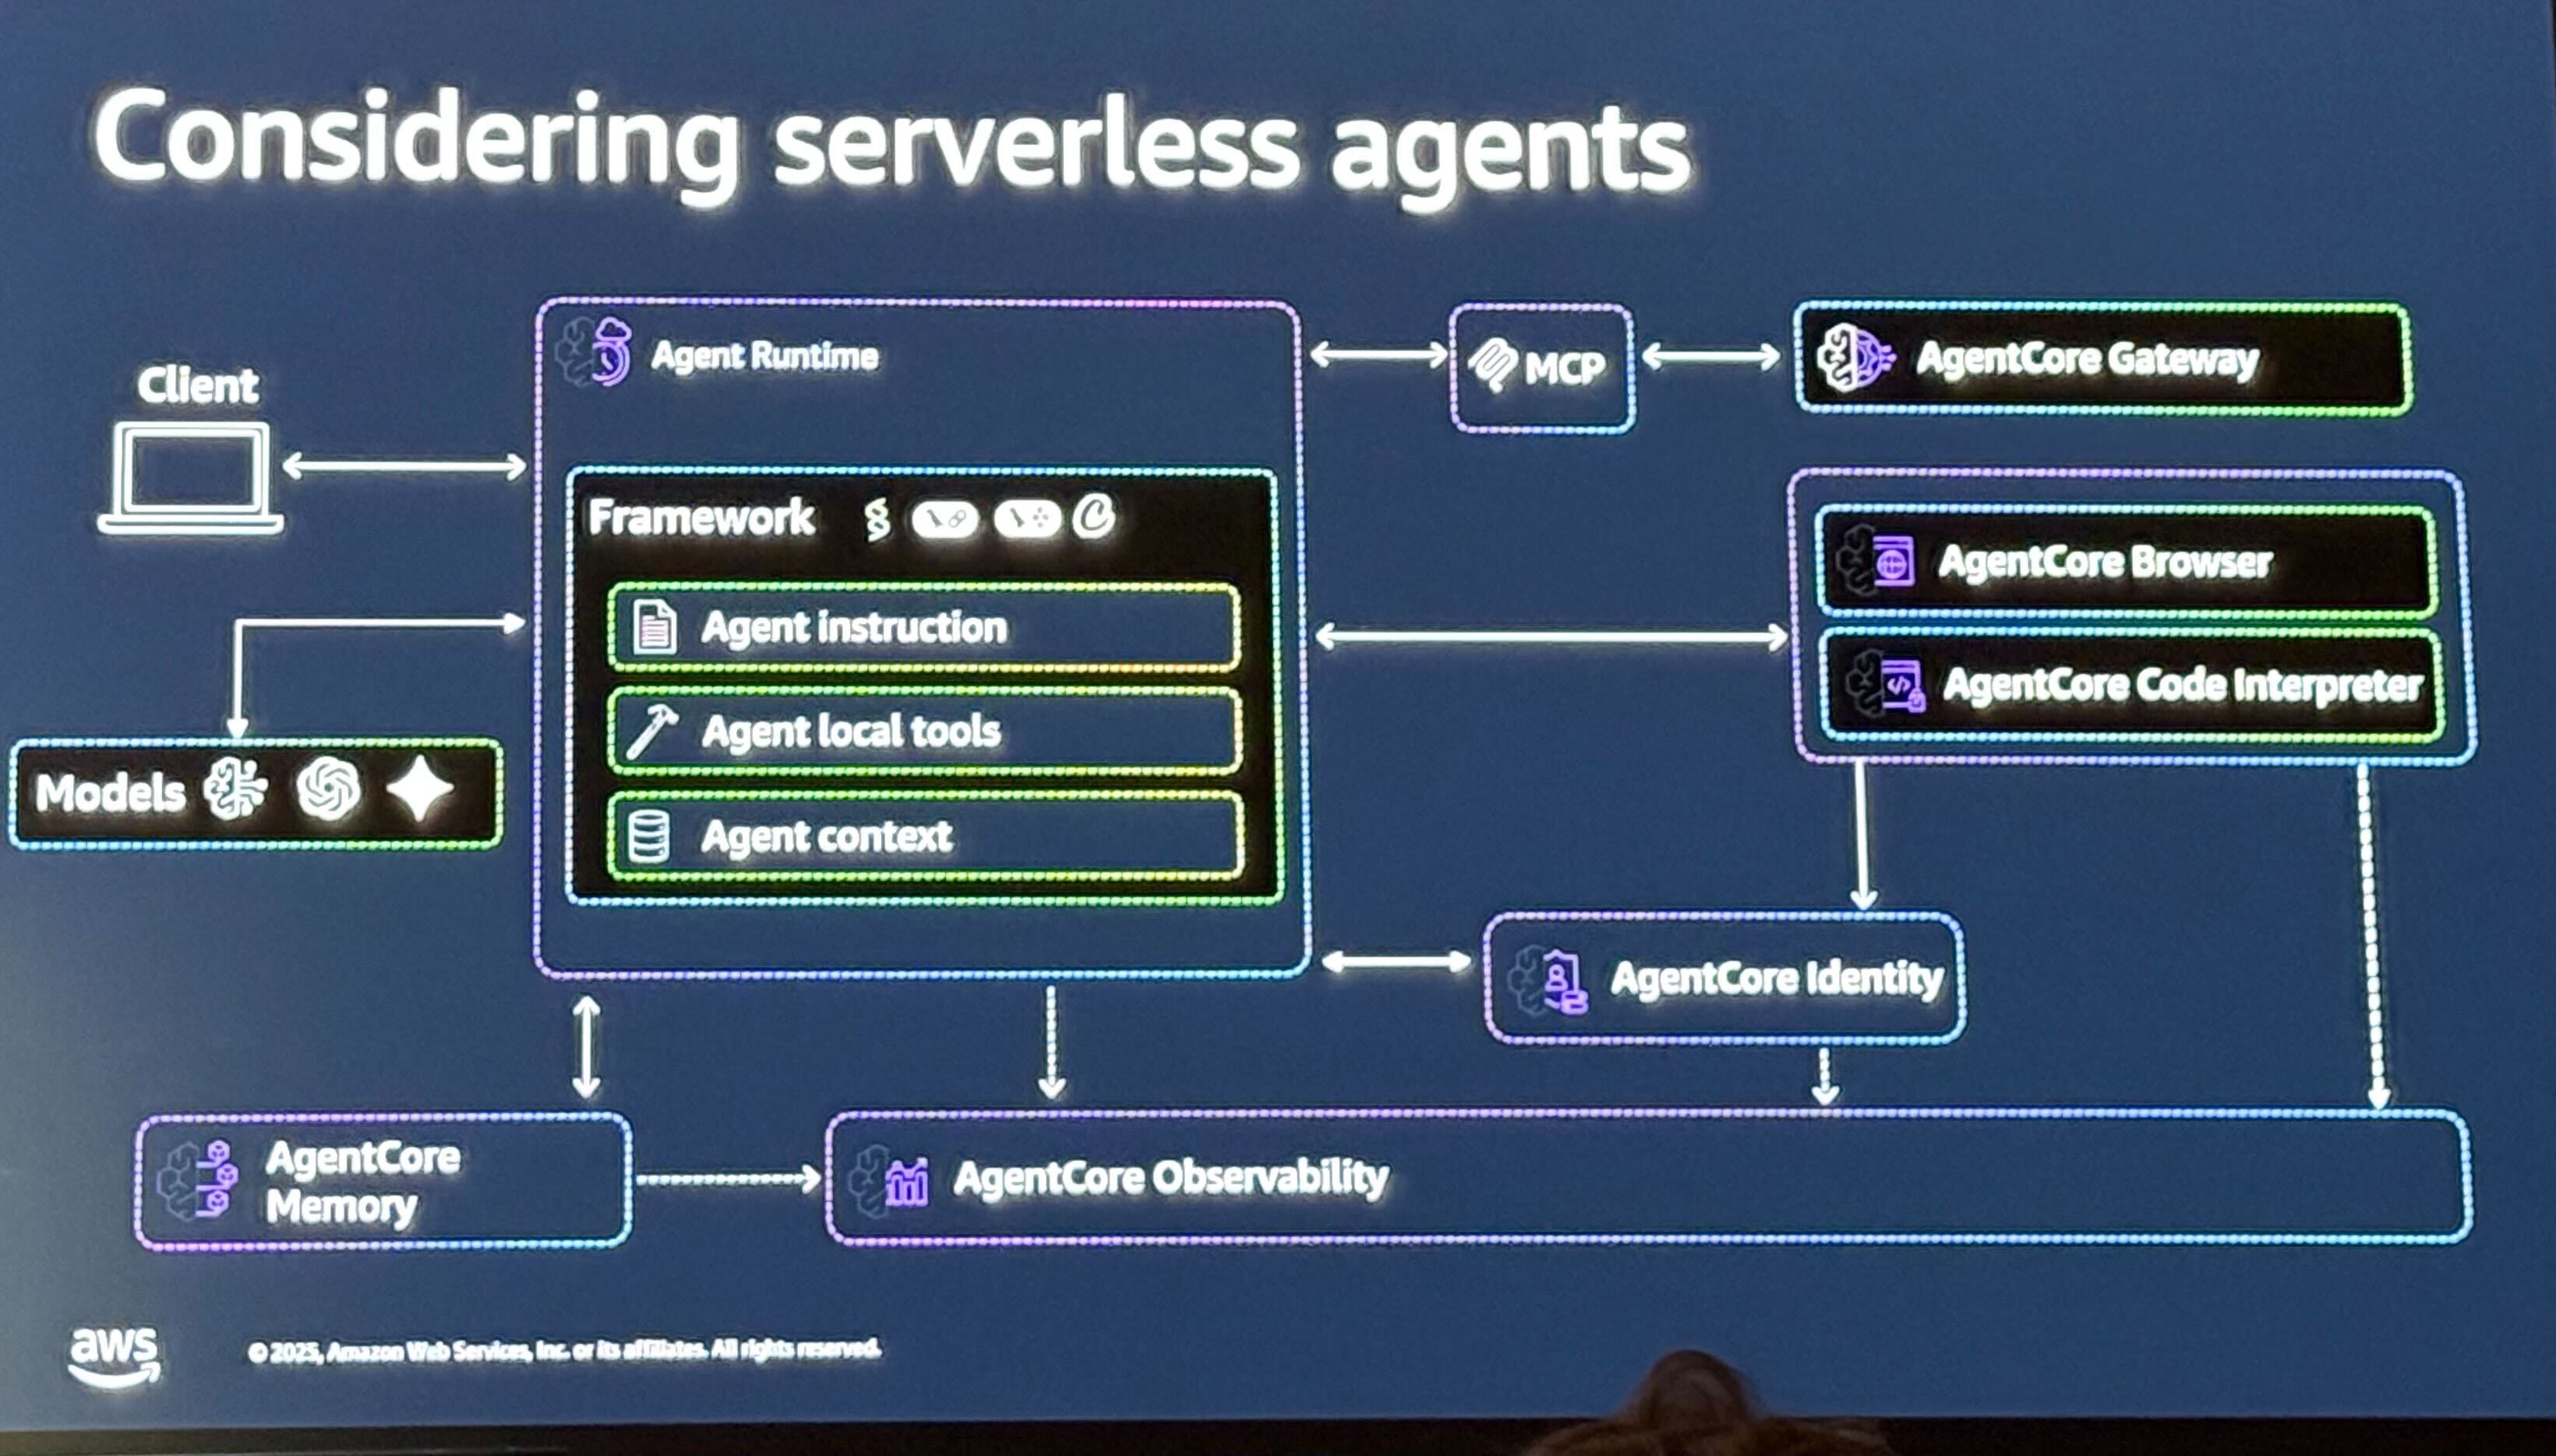
This session also walked through inbound and outbound auth for Amazon Bedrock AgentCore Identity, which is expected to become more and more relevant as serverless applications start using AI agents as a part of their stack.
AgentCore Identity is a centralized identity and credential management service for AI agents and automated workloads, designed so that agents become first-class identities with their own permissions and securely managed credentials. It was launched to solve the specific problem of how agents authenticate to gateways and downstream tools in a way that is auditable, least-privilege, and aligned with familiar patterns like OAuth2 and IAM.
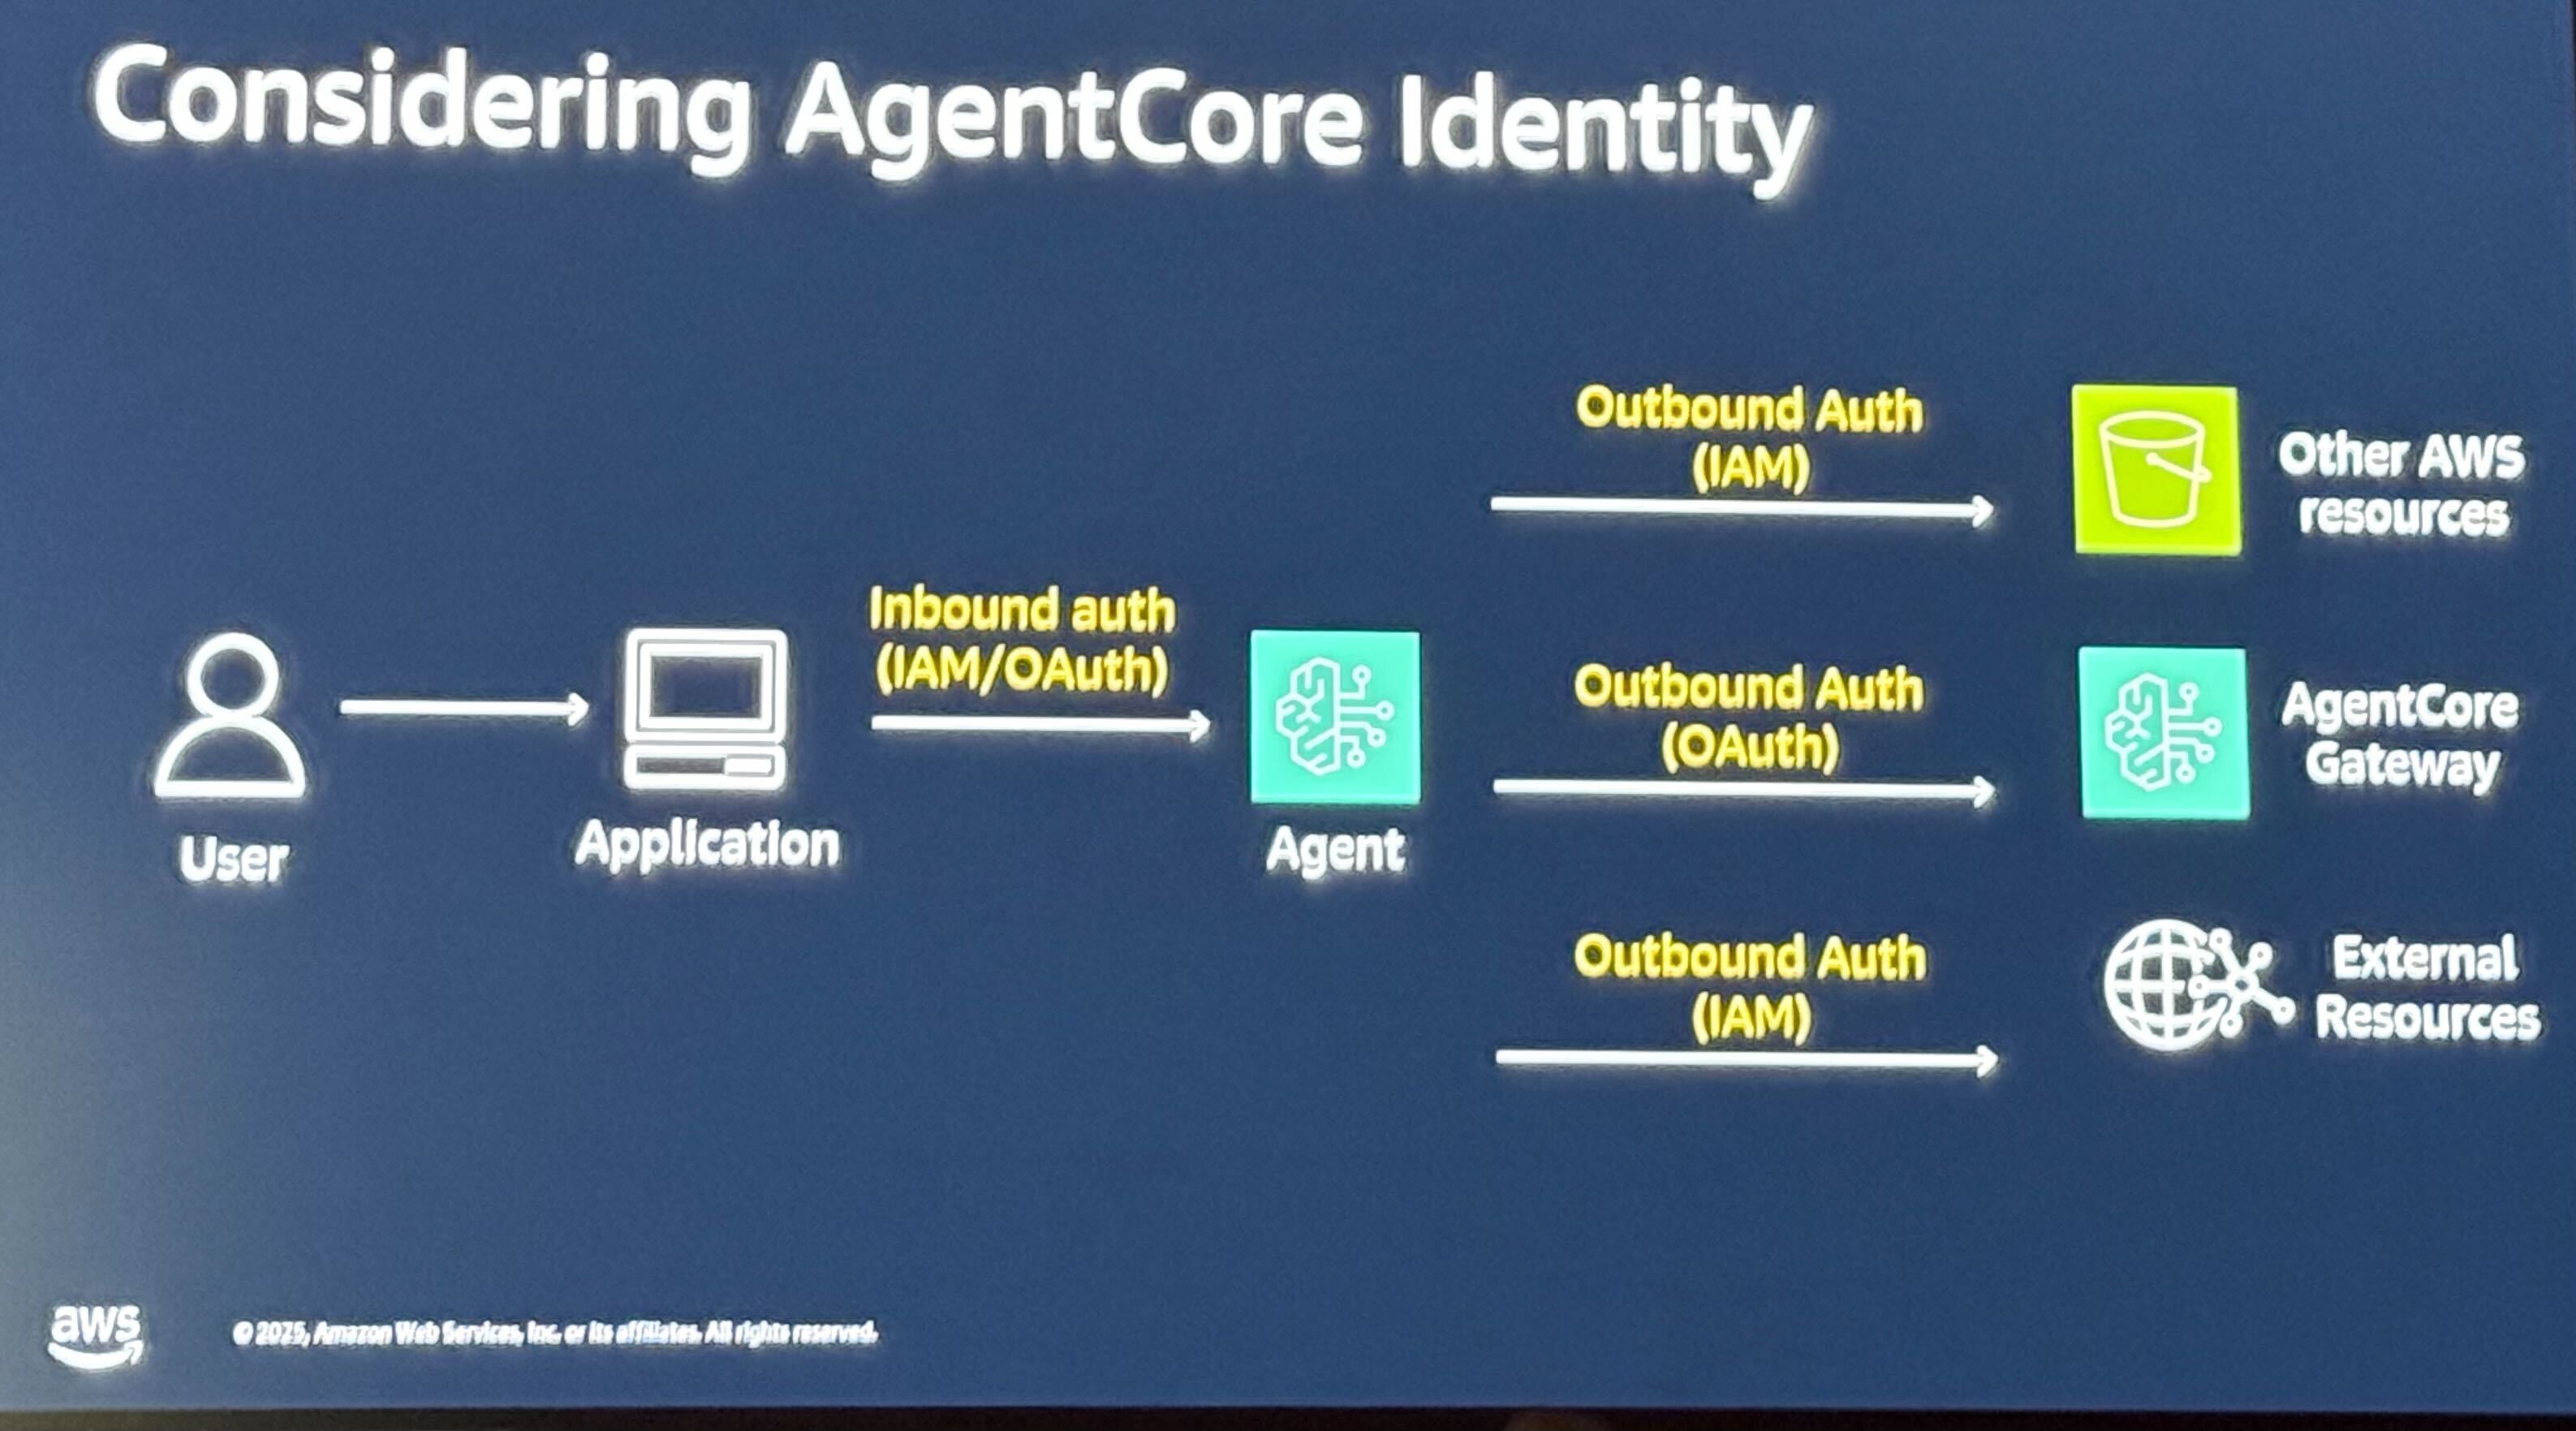
Inbound auth in AgentCore Identity focuses on *who* is allowed to invoke an agent or gateway: it validates requests using IAM, OAuth2/OIDC providers, and JWT verification so that only trusted users, services, or other agents can reach your agent endpoints.
Outbound auth then controls *what* the agent is allowed to call once it is running by centrally managing OAuth clients, API keys, and IAM roles and issuing scoped credentials for downstream APIs and SaaS integrations.
In the context of serverless security, this dual model makes a lot of sense: inbound auth mirrors API Gateway and Lambda authorizers for protecting entry points, while outbound auth mirrors tightly scoped execution roles and resource-based policies, giving agents the minimum access they need with a clear audit trail. You can see a visualization of this below:
## Final thoughts
This session did more than list patterns; it connected them into a coherent security model for serverless and agentic AI workloads. It was also a strong confirmation that the architectures and recommendations we’re bringing to clients are fully aligned with where AWS security best practices are today and where they’re heading next.
If your organization needs help figuring out how to make serverless applications on AWS more secure, [contact us](https://ipponusa.com/contact/?__hstc=223023812.a87ab388273ac2daddf8e536df74e9ca.1763987705654.1763987705654.1764094754002.2&__hssc=223023812.6.1764094754002&__hsfp=2901071483) and we will be happy to help.
## Related Articles
##### [ Serverless • December 11, 2025 AWS re:Invent 2025: Understanding the Event and the Major Innovations That Will Transform the Cloud 9 min read](https://blog.ippon.tech/aws-reinvent-2025-understanding-the-event-and-the-major-innovations-that-will-transform-the-cloud)
##### [ Serverless • December 4, 2025 Cloud Platform Engineering: Product Mindset 7 min read](https://blog.ippon.tech/cloud-platform-engineering-product-mindset)
### Comments
### Subscribe to Our Blog!
Stay informed with the latest insights and updates by signing up for our weekly blog newsletter – delivered straight to your inbox!
[Back to blog homepage »](https://blog.ippon.tech/)
Ippon is a consulting and expertise firm, who is convinced that technology is a source of progress for society. We help our clients leverage their digital assets to design an appropriate strategy and deploy their transformation roadmap at scale.
#### Navigation
- [Home](https://ipponusa.com/)
- [About](https://ipponusa.com/about-us/)
- [Services](https://ipponusa.com/services/)
- [Blogs](https://blog.ippon.tech/?__hstc=223043268.1036d82247623b329dfefe4e92697801.1714729179243.1714729179243.1714729179243.1&__hssc=223043268.2.1714729179244&__hsfp=803678701)
- [eBooks](https://ipponusa.com/ebooks/)
- [The Data Pour](https://info.ippon.tech/the-data-pour?__hstc=223043268.1036d82247623b329dfefe4e92697801.1714729179243.1714729179243.1714729179243.1&__hssc=223043268.2.1714729179244&__hsfp=803678701)
[Contact Us](https://ipponusa.com/contact/)
[Join Us](https://ipponusa.com/careers/)
#### Services
- [Data & Analytics](https://ipponusa.com/service/data-analytics/)
- [Cloud Strategy](https://ipponusa.com/service/cloud-strategy/)
- [Artificial Intelligence](https://ipponusa.com/service/artificial-intelligence/)
- [Operating Model](https://ipponusa.com/service/operating-model/)
- [Platform Modernization](https://ipponusa.com/service/platform-moderization/)
- [Product Innovation](https://ipponusa.com/service/product-innovation/)
#### Ippon International
- [France](https://fr.ippon.tech/?__hstc=223043268.1036d82247623b329dfefe4e92697801.1714729179243.1714729179243.1714729179243.1&__hssc=223043268.2.1714729179244&__hsfp=803678701)
- [Australia](https://au.ippon.tech/?__hstc=223043268.1036d82247623b329dfefe4e92697801.1714729179243.1714729179243.1714729179243.1&__hssc=223043268.2.1714729179244&__hsfp=803678701)
- #### Contact
- Ippon Technologies
[3431 West Leigh Street Richmond, VA 23230, USA](https://maps.app.goo.gl/RySm6SAwZnsxeiLz9)
- [(844) 477- 6687](tel:8444776687)
- [Sales@ipponusa.com](mailto:Sales@ipponusa.com)
©Copyright 2024 Ippon USA. All Rights Reserved. | [Terms and Conditions](https://ipponusa.com/privacy-policy/) | [Privacy Policy](https://ipponusa.com/privacy-policy/) | [Website by Skol Marketing](https://skolmarketing.com/)
```json
{
"@context" : "https://schema.org",
"@type" : "BlogPosting",
"author" : {
"@type" : "Person",
"name" : "Iryna Chmelyk",
"url" : "https://blog.ippon.tech/author/iryna-chmelyk"
},
"dateModified" : "2025-12-08T18:25:45.917Z",
"datePublished" : "2025-12-08T07:30:00.000Z",
"headline" : "Security Recommendations of Serverless Applications Deep Dive",
"image" : [ "https://blog.ippon.tech/hubfs/Ippon%20copy-2.jpg" ],
"mainEntityOfPage" : {
"@id" : "https://blog.ippon.tech/security-recommendations-of-serverless-applications-deep-dive",
"@type" : "WebPage"
},
"publisher" : {
"@type" : "Organization",
"logo" : {
"@type" : "ImageObject",
"url" : "https://blog.ippon.tech/hubfs/logo_SVG.svg"
},
"name" : "Ippon Technologies"
}
}
```